Compliance
10 HIPAA-Aware Design Choices in TargetFlo
Ten design choices behind TargetFlo's HIPAA-aware architecture: a separate PHI schema, application-layer encryption, role-based access, audit logs, hashed signed notes, an SMS PHI guard, encrypted storage, NPP tracking, clinician-signed AI drafts, and a BAA.
TargetFlo Team 1 min read
"HIPAA compliant" on a vendor website tells you very little. What matters is how the software is built. These are ten choices TargetFlo made on purpose.
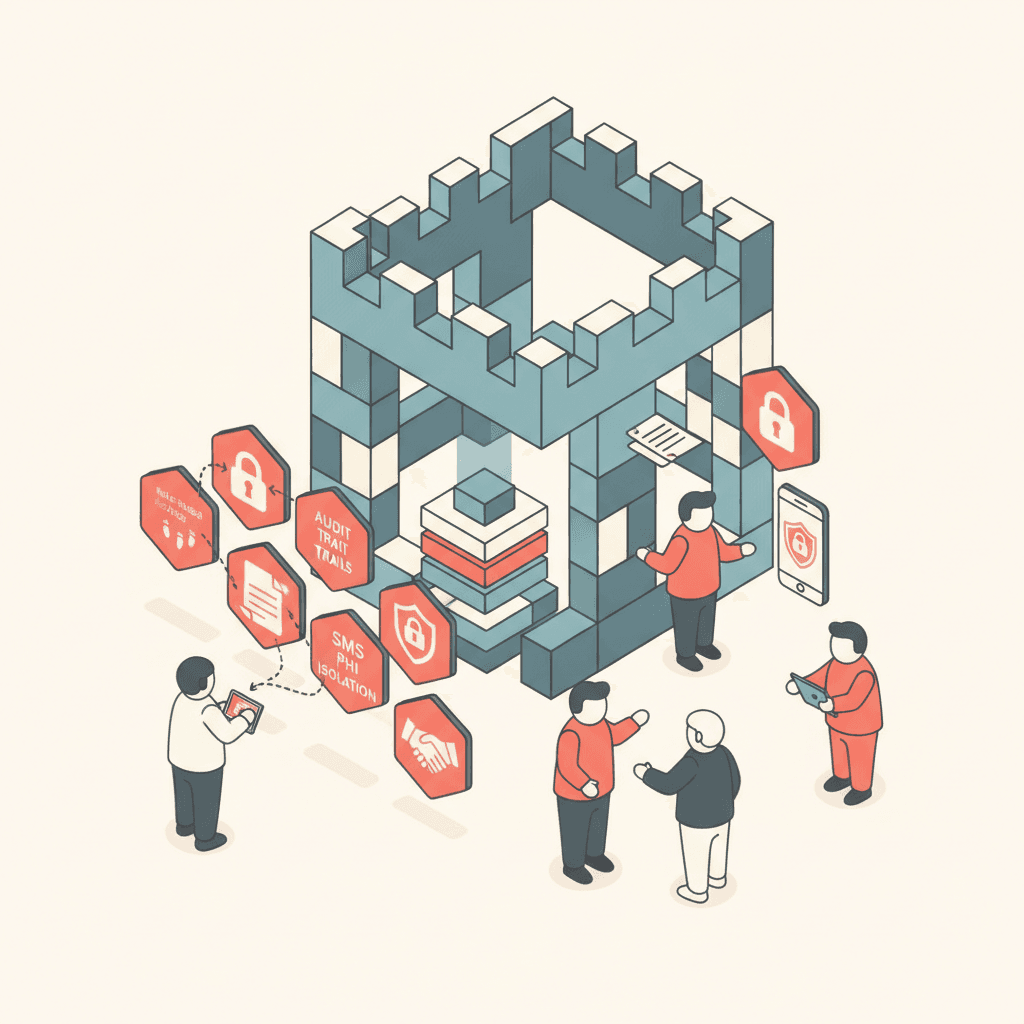
- PHI lives in its own database schema, separate from operations, identity, and billing.
- PHI fields are encrypted at the application layer before they reach the database.
- Role-based access on every screen and API.
- An audit log of PHI access, overrides, and denied attempts.
- Signed session notes are hashed and never change; corrections are signed addenda.
- A PHI guard checks outbound SMS for identifiers before it sends.
- Encrypted document storage on Google Cloud.
- Notice of Privacy Practices acknowledgment is tracked per guardian.
- AI drafts are suggestions — clinicians review, edit, and sign.
- A BAA is available before any PHI enters the product.
Read more on Security and HIPAA-aware software for ABA.
- HIPAA aware ABA software
- HIPAA compliant ABA practice management
- ABA software security
- PHI encryption
See it in TargetFlo
Move intake out of the fax inbox
Book a 30-minute demo and we’ll map your referral flow to the 9-stage pipeline, connect your fax provider, and show eligibility checks at intake.
Book a DemoFAQ